Verified Case Files
Declassified summaries from actual victims. Analyze the operational mechanics of syndicates to fortify your own defenses.
⚠️ Operational Similarity Warning
The case studies documented below follow strict psychological and technical patterns utilized by active threat groups.
If your current situation mirrors any of these profiles, you must halt all fund transfers immediately.
"The psychological manipulation was flawless. It wasn't just my wallet they emptied, it was my trust." — Sarah, 49
Sarah was engaged via a dating platform by a fabricated persona named "David." After establishing a deep emotional rapport over 6 weeks, David introduced a "proprietary" cryptocurrency trading node. After a successful $5,000 test yielding a $1,000 withdrawal, Sarah liquidated her savings and took out loans totaling $100,000. Upon attempting to withdraw her capital, the platform initiated a lock, demanding a $15,000 "blockchain tax," followed by a secondary $10,000 "liquidity fee." Upon refusal, the platform and the operative vanished.

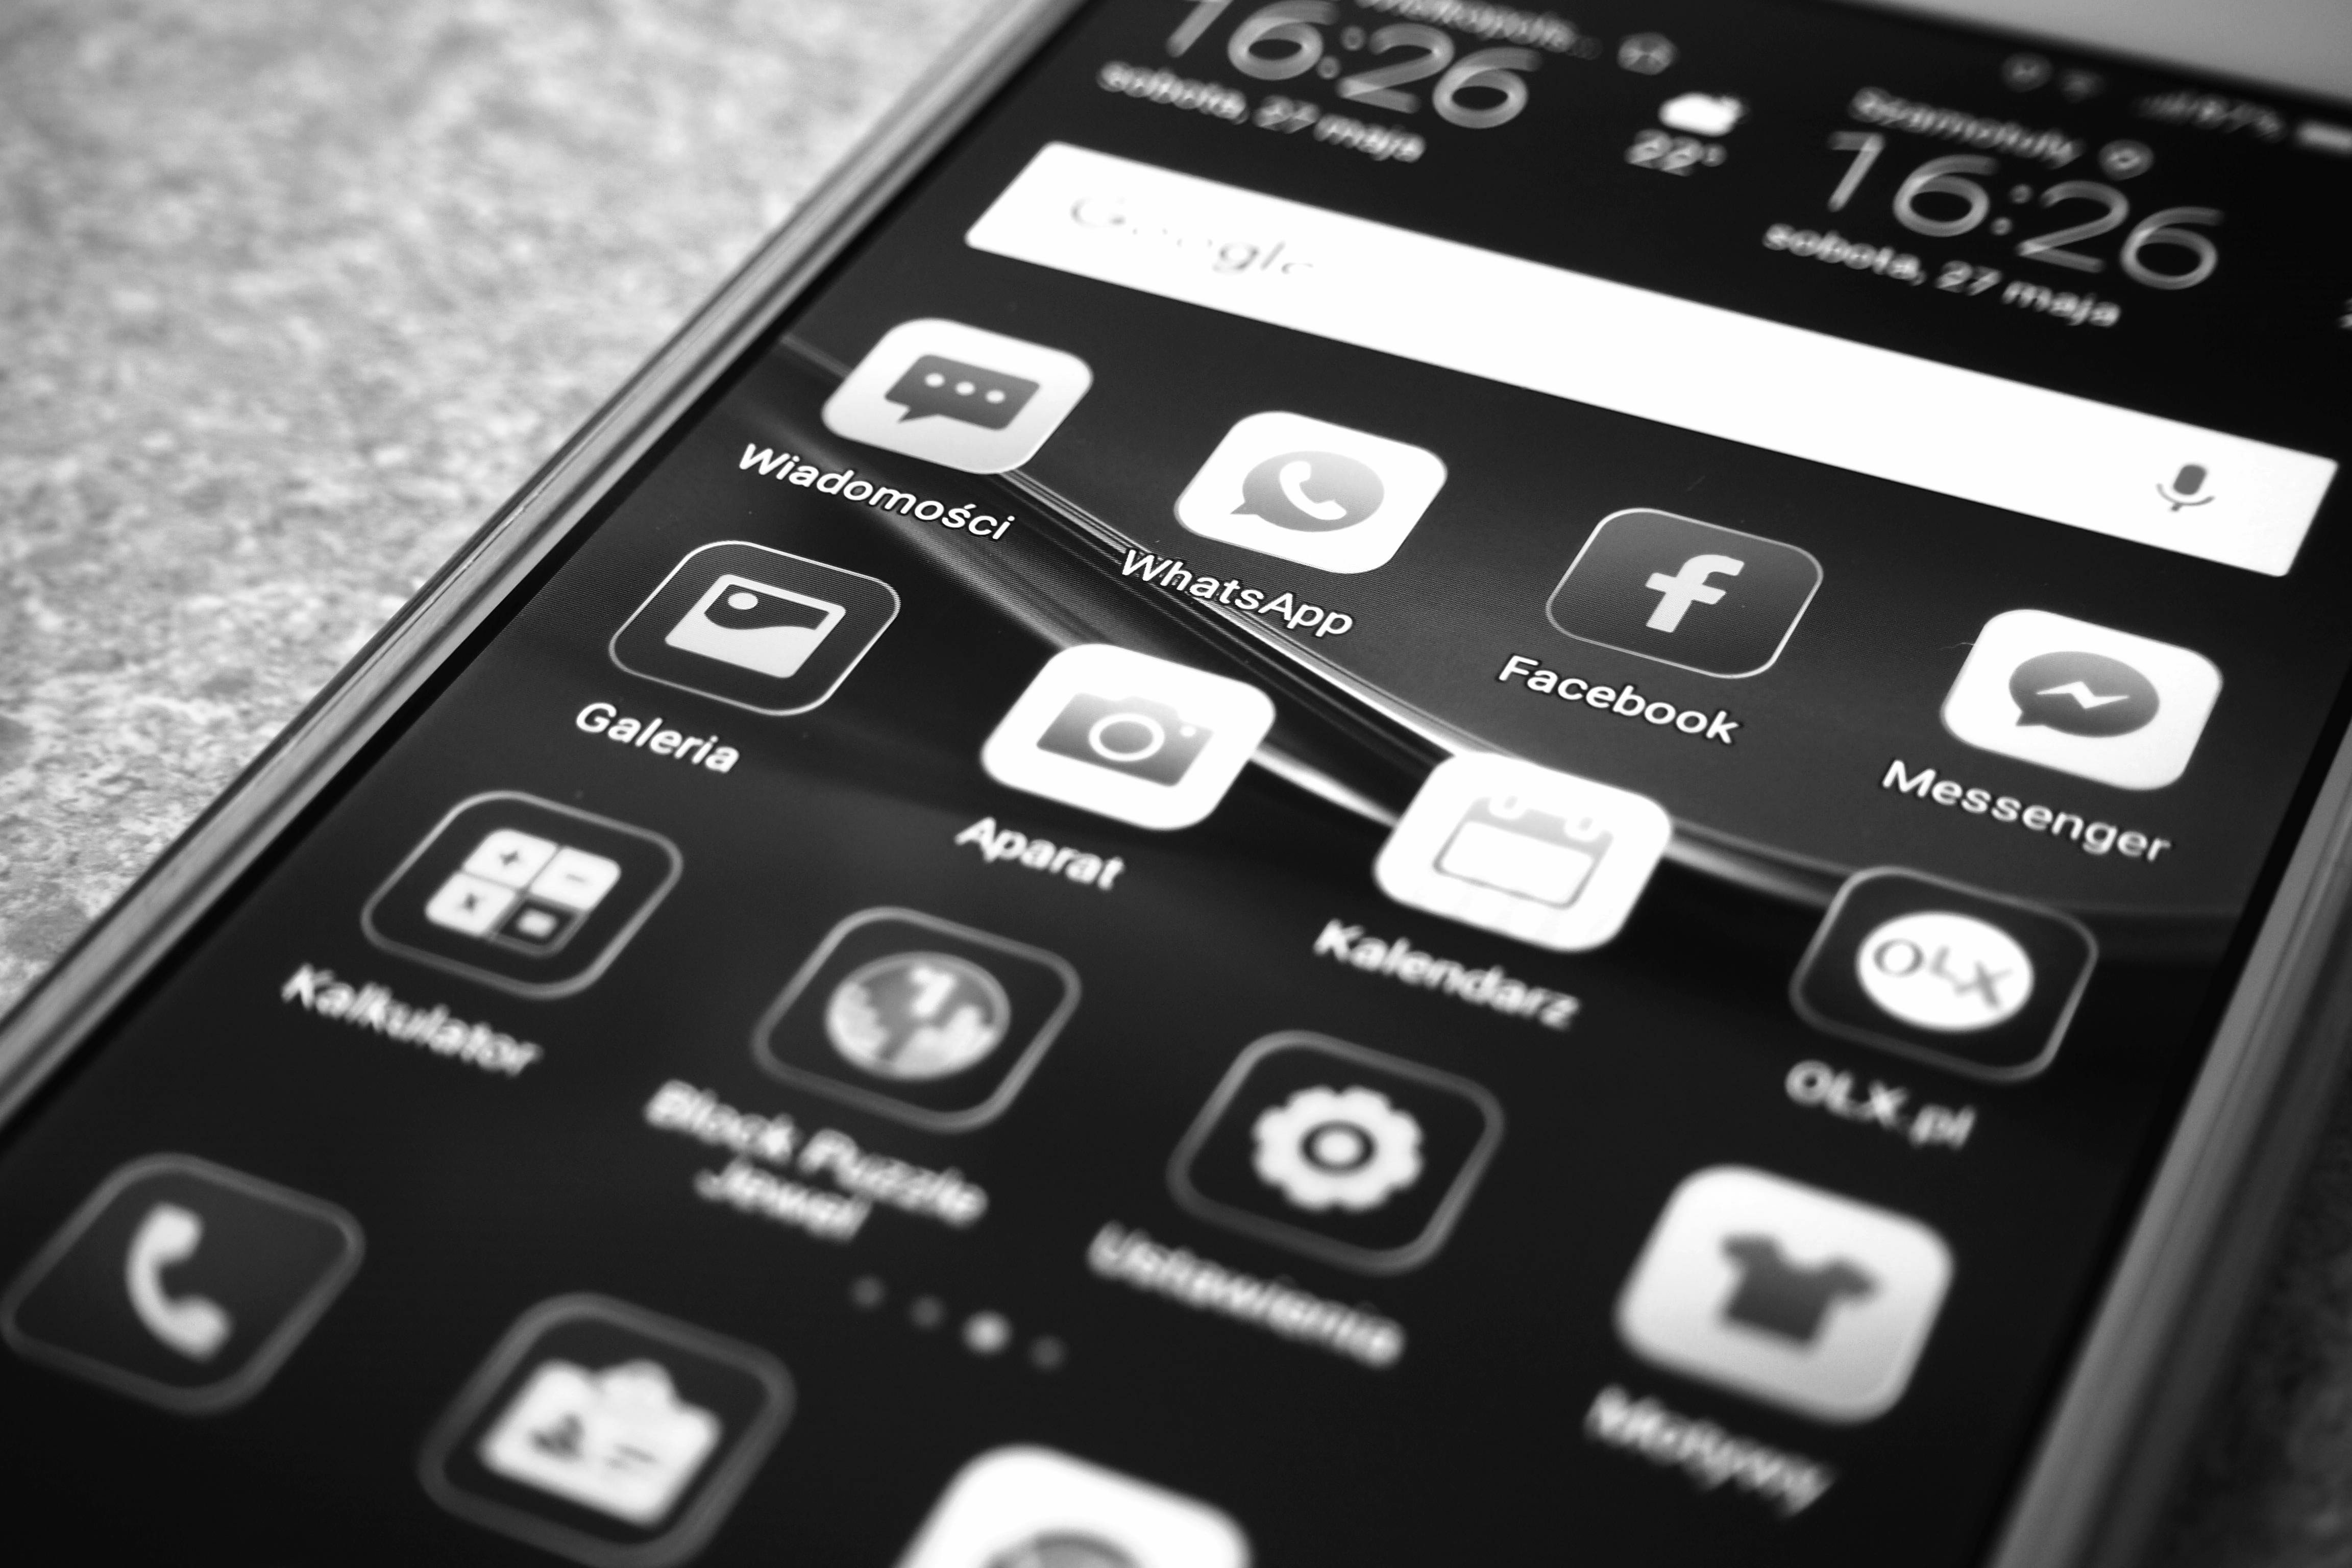
"A structured sequence of micro-rewards blinded me to the macro-extraction." — Mike, 28
Mike was targeted via WhatsApp by a fraudulent recruitment agency offering a remote gig: "Like media content to generate commissions." An initial 10 tasks yielded a legitimate $200 payout. The operative then introduced "VIP tasks" requiring capital deposits to unlock higher yields. $500 yielded $600. $2,000 yielded $2,400. Upon depositing $10,000, his account was frozen for a "protocol violation." Unfreezing required a $15,000 penalty. After complying, a second $15,000 was demanded, resulting in total capital loss.
"The caller utilized federal statutes to induce panic. Logic was completely bypassed." — Robert, 67
Robert received a call from a spoofed number matching the Federal Investigations Unit. The operative, "Agent Miller," informed Robert that his identity had been compromised and utilized in international money laundering. To prevent immediate asset seizure and arrest, Robert was instructed to transfer his liquidity to a "Federal Protection Node." Official-looking subpoenas were emailed as validation. Robert wired $89,000. Subsequent attempts to contact the agent failed.
"The dashboard analytics were a complete simulation. None of the liquidity was real." — David, 45
David interacted with a sponsored social media advertisement for a high-yield algorithmic trading desk. An initial $1,000 deposit reflected a 10x ROI on the platform's dashboard within weeks. Encouraged by the metrics, David injected an additional $150,000, which the interface displayed as exceeding $1 Million in value. Upon liquidation request, the system triggered a 20% "Cross-Border Withdrawal Tariff." David paid an additional $62,000 before the domain was abruptly taken offline.
"Threat actors rely on absolute predictability. By analyzing their blueprints, you remove their primary weapon: the element of surprise."
✅ Successful Countermeasures
- ✓ Initiated banking fraud protocols within 24-48 hours.
- ✓ Archived complete ledger data and encrypted chat histories.
- ✓ Notified institutional fraud departments immediately.
- ✓ Engaged verified intelligence teams before executing secondary payments.
❌ Fatal Vulnerabilities
- ✗ Delaying institutional reporting due to embarrassment.
- ✗ Executing secondary "extortion" payments to unlock frozen assets.
- ✗ Deploying capital to unverified "recovery hackers" on social platforms.
- ✗ Deleting communication logs to erase the memory of the event.
Does Your Situation Mirror These Profiles?
If you recognize the operational tactics listed in these files, you must act rapidly. The window for asset retrieval is highly time-sensitive.